Managed switch graphic with a warning about unpatched D-Link DGS-3130 zero-days

D-Link DGS-3130 Unpatched Zero-Days: Disable DDP Now While Firmware Is Still Coming

D-Link published an interim security advisory today, November 6, 2026, warning that multiple unpatched vulnerabilities hit its DGS-3130-30TS managed Gigabit stackable switches, with other DGS-3130 models and even other switching platforms still under investigation. The bugs, found by Spectrum Community Solutions network engineer Giresh Kumar Enugu, sit in the D-Link Discovery Protocol (DDP) and in […]

Continue Reading
Network switch graphic warning about the Zyxel GS1900 zero-day CVE-2026-107441

Zyxel GS1900 Zero-Day CVE-2026-107441: Nearly 1,000 Switches Hacked After the June Patch Failed

Zyxel has patched a zero-day in its popular GS1900 series of smart managed switches after attackers used it to compromise nearly 1,000 devices worldwide and steal configurations and hashed root credentials. The flaw, tracked as CVE-2026-107441 and scored CVSS 8.8, is an out-of-bounds write in the switch web management CGI that lets a LAN-based, unauthenticated […]

Continue Reading
Clock graphic showing a one-hour drift with the text Canada Time Zones Hit Microsoft 365

Canada’s Time Zone Change Hits Microsoft 365: What Admins Need to Fix in Outlook, Teams and Power Automate

When most of North America set its clocks back on November 1, 2026, large parts of western and central Canada stayed put. British Columbia, Alberta and Manitoba moved to permanent daylight time, locking in fixed offsets of UTC−07:00, UTC−06:00 and UTC−05:00, with affected parts of the Northwest Territories (including Yellowknife and Inuvik) following Alberta and […]

Continue Reading
Illustration of a grid of expert blocks with a few highlighted, representing a Mixture-of-Experts model

Mistral Large 4 Goes Open Weight: A 1-Trillion-Parameter Model You Can Run on Your Own Hardware

Open-weight AI just got a lot bigger. On October 29, 2026, Paris-based Mistral AI released the weights of Mistral Large 4, nicknamed “Le Chonk”, a natively multimodal Mixture-of-Experts model with roughly 1 trillion total parameters, 49 billion active per token, and a 1-million-token context window. Mistral calls it the best open-weight model for coding, it’s […]

Continue Reading
Illustration of an extension marketplace list with one malicious entry and a reverse SSH tunnel command

Trojanized Claude Code Extension in Cursor’s Marketplace: An SSH Backdoor That Survives Uninstall

For about 11 hours on October 29, 2026, developers who installed or auto-updated Anthropic’s Claude Code extension from the Cursor editor’s extension marketplace got something extra: a tampered build, versions 2.1.312 and 2.1.313 for Windows and macOS, that tried to plant a persistent SSH backdoor. Cursor says the malicious package was live from about 2:27 […]

Continue Reading
Illustration of the WordPress logo above a core update progress bar, representing the CVE-2026-119977 upgrade race condition

WordPress 7.1.4 Upgrade-Window RCE CVE-2026-119977: Attackers Are Racing Your Updates

WordPress shipped version 7.1.4 on October 28, 2026, a short-cycle security release that Wordfence says fixes 22 security vulnerabilities, and attackers wasted no time going after the worst of them. CVE-2026-119977 (CVSS 8.1 per Wordfence) is an unauthenticated remote code execution race condition in the core upgrade process that affects every release from 4.7 through […]

Continue Reading
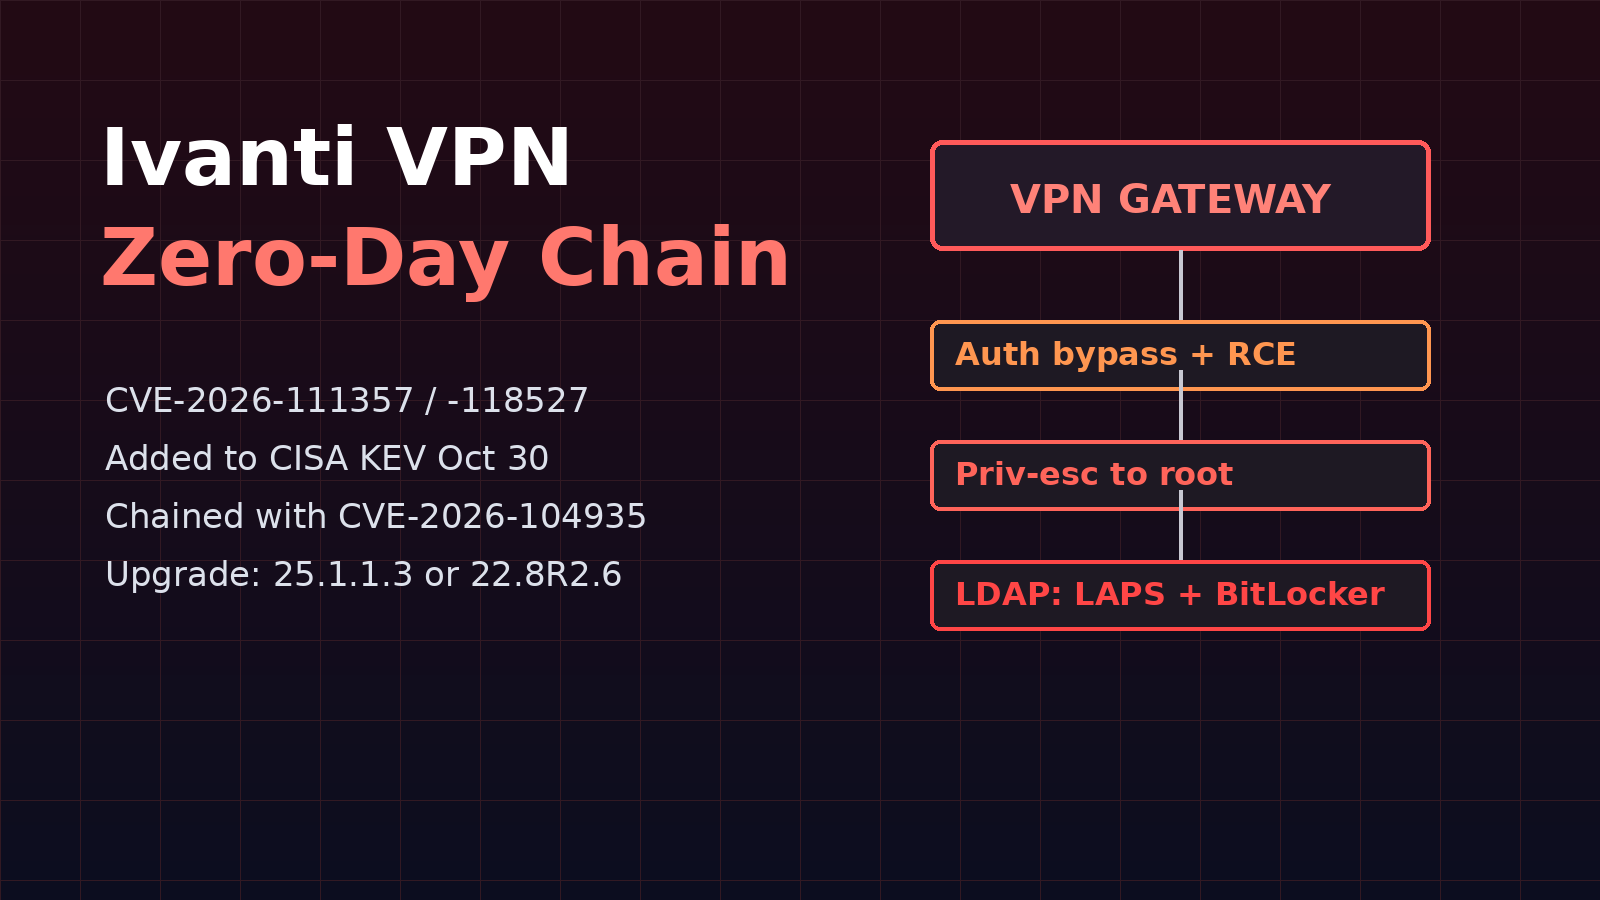
Illustration of an Ivanti VPN gateway exploit chain leading from authentication bypass to root and Active Directory secret theft

Ivanti Connect Secure Zero-Day Chain: Two More Exploited Flaws Mean Your October Patch Wasn’t Enough

If you patched your Ivanti Connect Secure VPN appliances in mid-October and moved on, you need to go back. On October 29, 2026, Ivanti updated its advisory with two more vulnerabilities, CVE-2026-111357 and CVE-2026-118527, that complete the zero-day chain attackers used to get unauthenticated root on fully patched gateways, and on October 30 CISA added […]

Continue Reading
Illustration of GitLab CI regex rules with text reading GitLab CI Regex RCE, CVE-2026-97229, exploited in the wild

GitLab CVE-2026-97229 Exploited: Max-Severity CI Regex Flaw Hit Alpine Linux, and Ruby Needs Patching Too

A maximum-severity GitLab flaw has moved from patch notes to real-world attacks. CVE-2026-97229 (CVSS 10.0), an integer overflow in how GitLab compiles regular expressions in CI/CD configurations, was used against Alpine Linux’s GitLab instance on October 20 and 21, 2026, just over a week after GitLab’s October 12 fix. CISA added the bug to its […]

Continue Reading