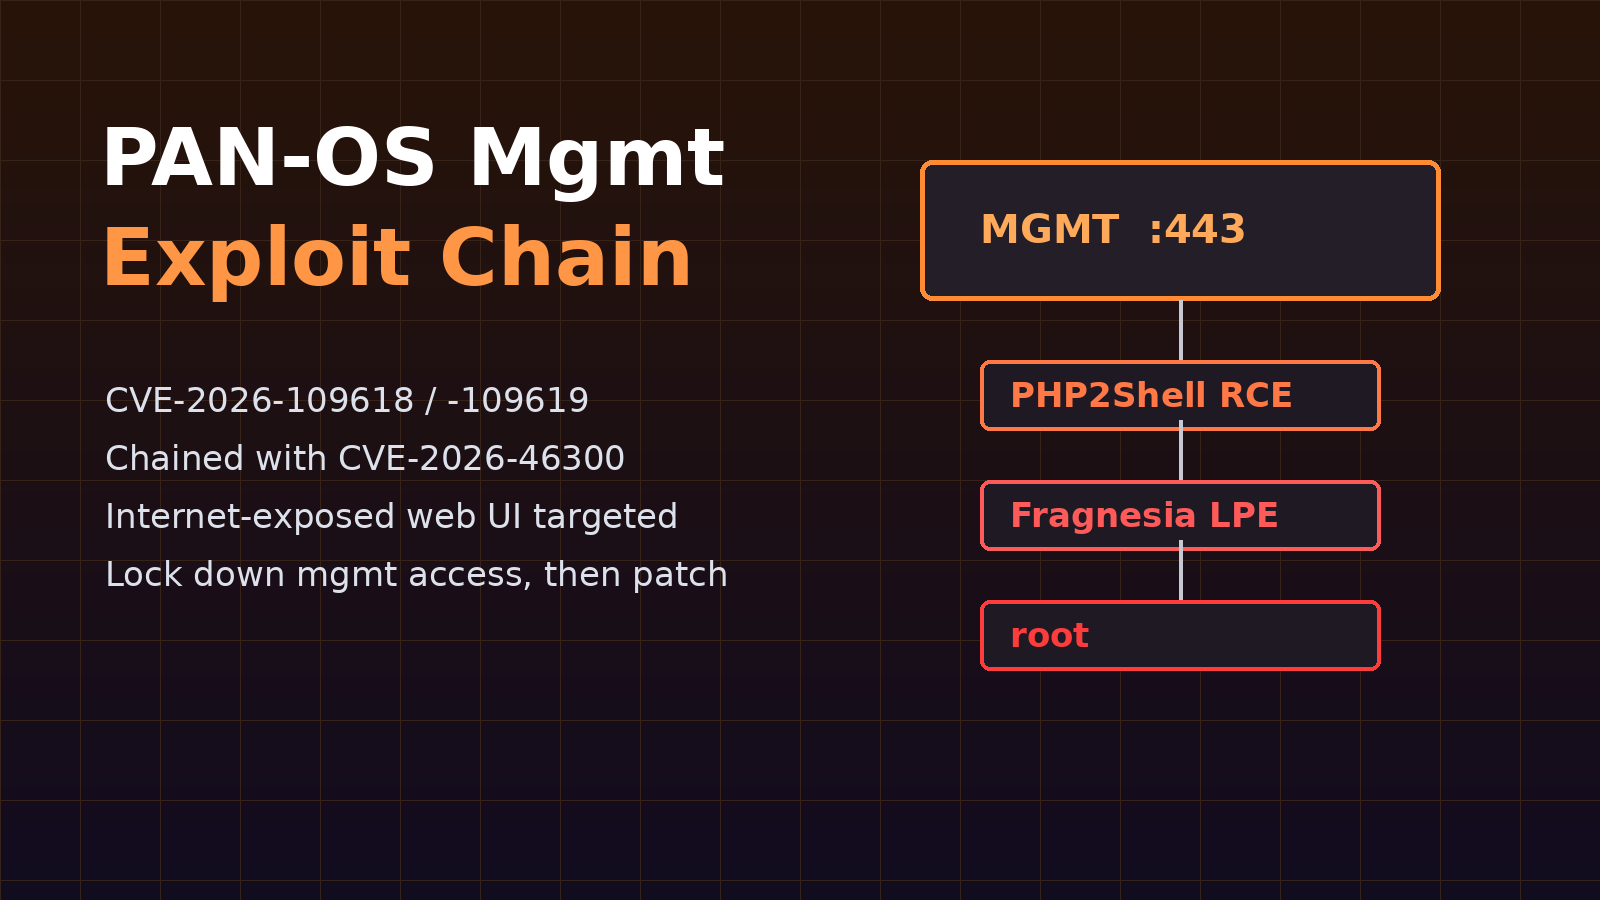
Illustration of a PAN-OS management interface exploit chain from PHP2Shell RCE to Fragnesia privilege escalation to root

PAN-OS PHP2Shell Attacks: Exploit Chain With Fragnesia Roots Internet-Exposed Firewalls

Palo Alto Networks confirmed on October 29, 2026 that attackers are actively exploiting the PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2), against PAN-OS management interfaces exposed to the internet. The update lands days after Israeli security firm Dream reported a suspected China-nexus operation that chained a custom PHP2Shell exploit with the Linux kernel bug Fragnesia […]

Continue Reading
Illustration of a server rack with a faded audit log, representing an ESXi logging bypass

VMware ESXi CVE-2026-41709: China’s WARP PANDA Used a ‘Low-Severity’ Logging Bug to Hide in Hypervisors

A VMware ESXi bug rated just 2.7 on the CVSS scale turns out to have been a zero-day weapon for one of China’s most capable espionage crews. CISA added CVE-2026-41709, an insufficient-logging flaw that lets an attacker with admin access perform certain operations without being logged, to its Known Exploited Vulnerabilities (KEV) catalog on October […]

Continue Reading
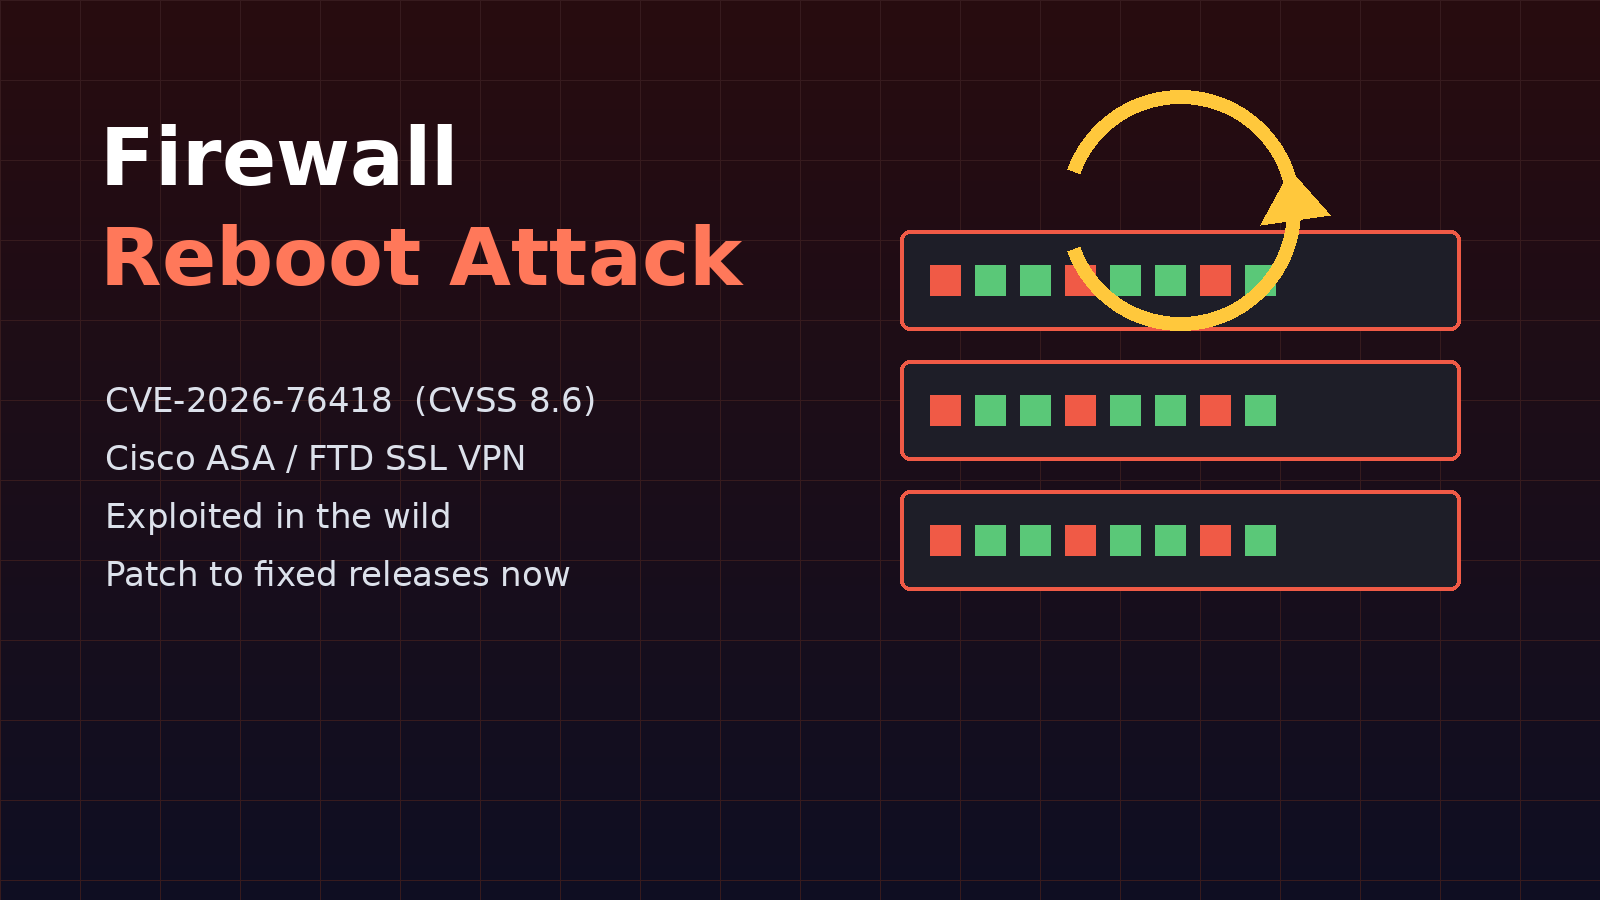
Illustration of a firewall appliance rebooting under attack, labeled CVE-2026-76418

Cisco ASA and FTD Zero-Day CVE-2026-76418: Exploited SSL VPN Flaw Crashes Firewalls on Demand

Cisco has patched a high-severity zero-day in its Secure Firewall ASA and Secure Firewall Threat Defense (FTD) software that attackers are already using to knock firewalls offline. Tracked as CVE-2026-76418 (CVSS 8.6, Cisco bug CSCwx26625), the flaw lives in the Remote Access SSL VPN service and lets an unauthenticated, remote attacker force the device to […]

Continue Reading
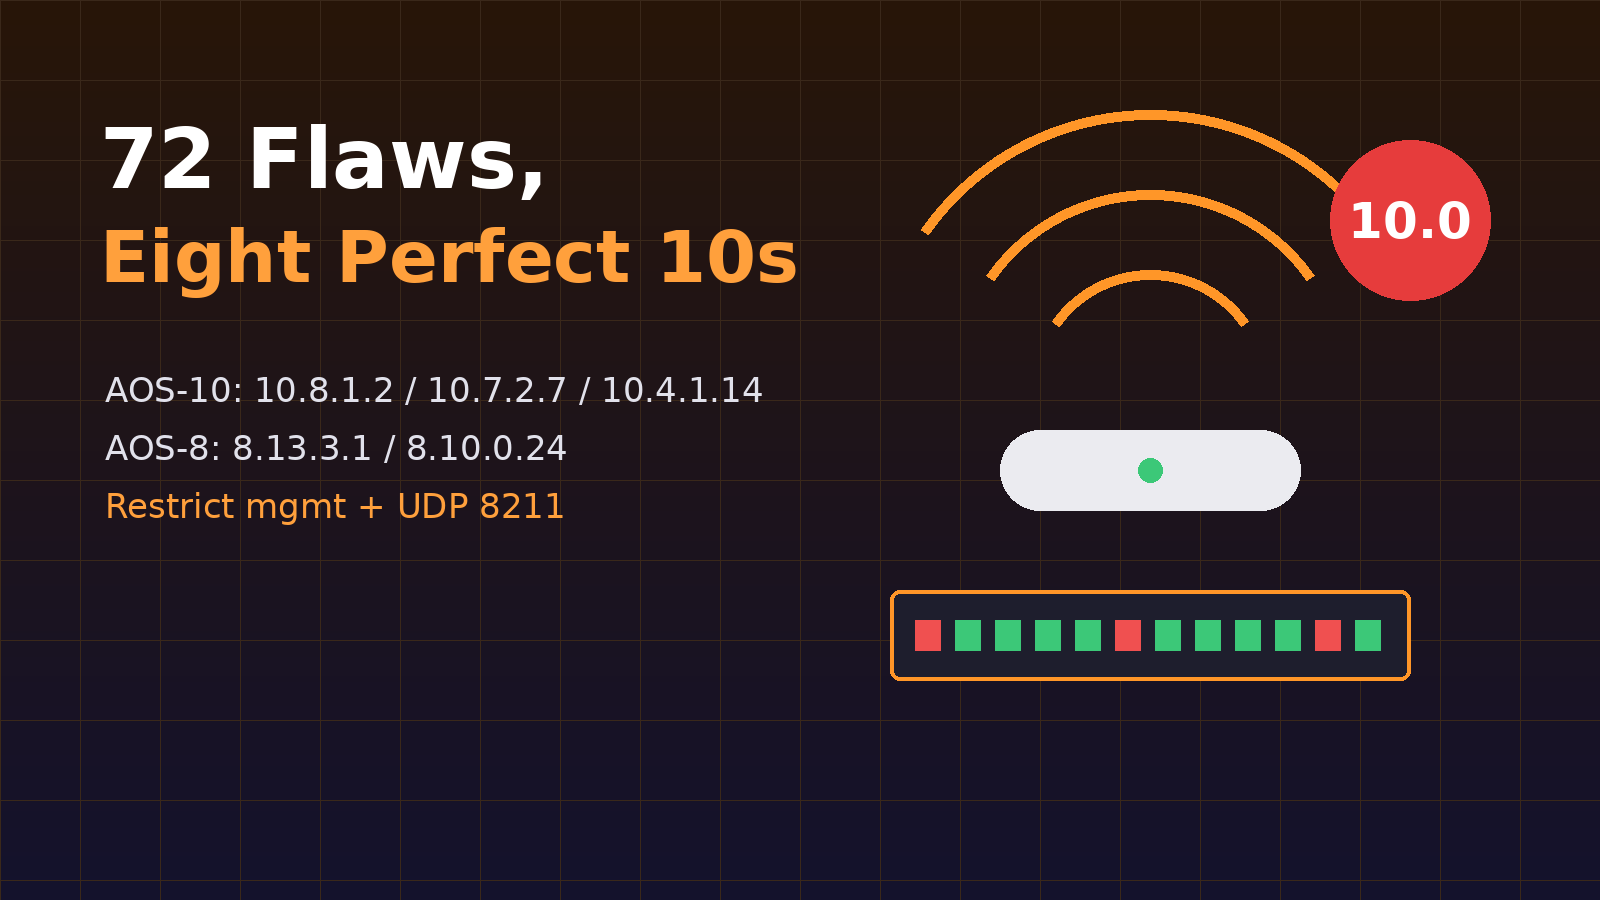
Illustration of a wireless access point and controller with a 10.0 severity badge and the text 72 Flaws, Eight Perfect 10s

HPE Aruba AOS-8 and AOS-10 Flaws: 72 Bugs and Eight Perfect-10 RCEs Put Wireless Controllers on Notice

HPE has released one of the biggest wireless security updates in recent memory, patching 72 vulnerabilities in ArubaOS (AOS-8 and AOS-10), the operating system behind Aruba Mobility Conductors, Mobility Controllers, Central-managed Gateways and access points. Eight of the flaws carry the maximum CVSS score of 10.0 and allow unauthenticated remote code execution, authentication bypass, command […]

Continue Reading
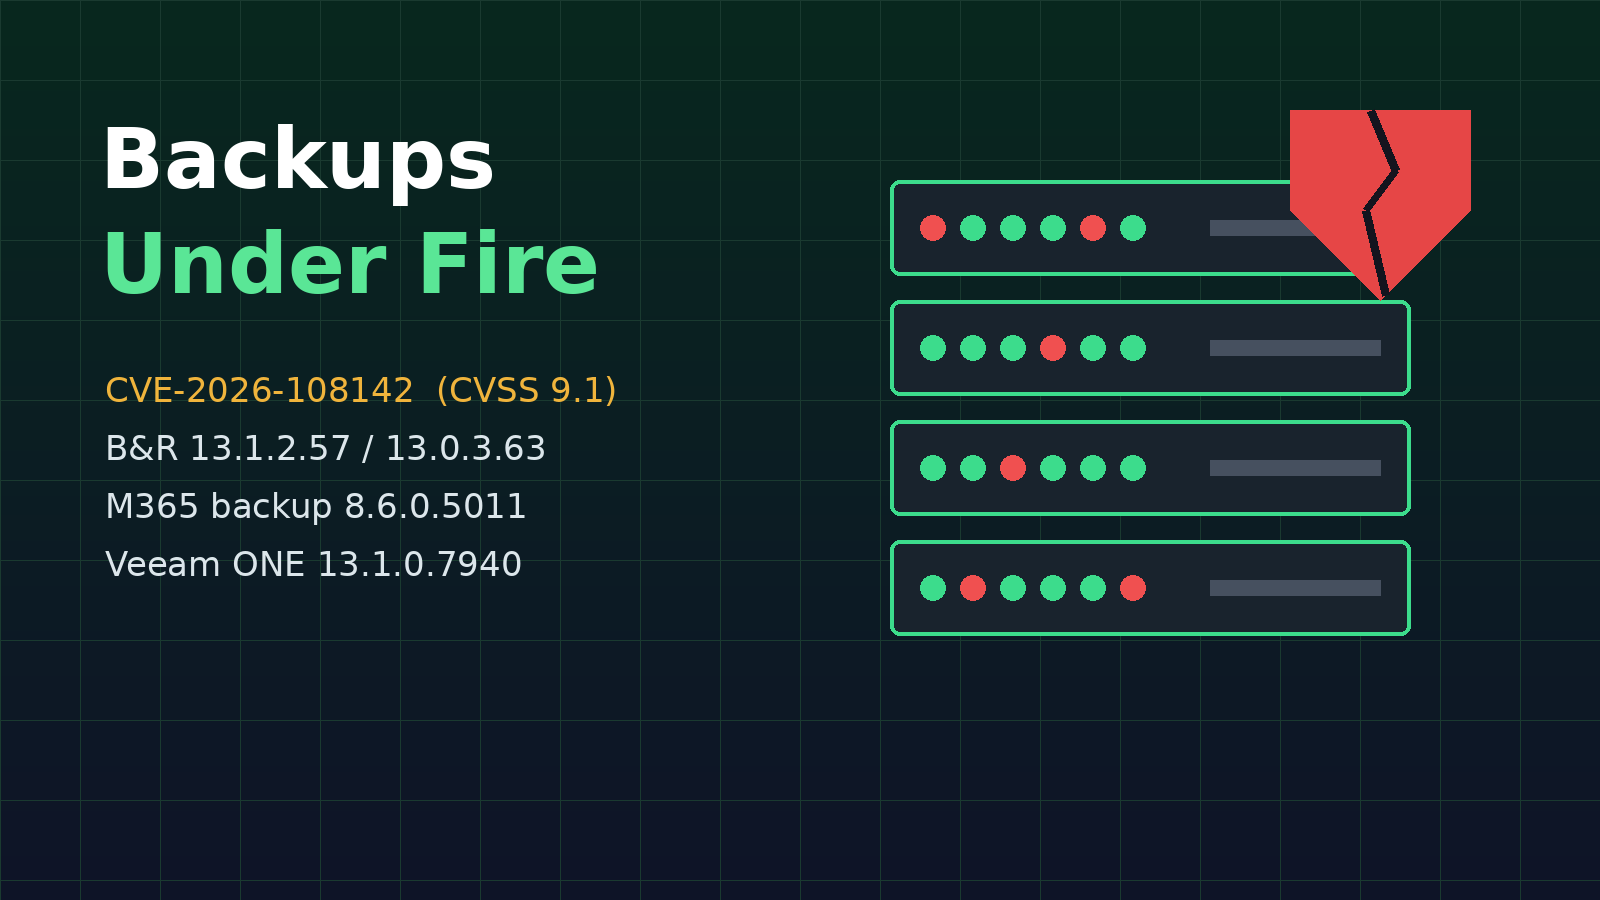
Illustration of backup server racks with a broken shield and the text Backups Under Fire listing Veeam fixed builds

Veeam CVE-2026-108142: Critical Backup & Replication and Microsoft 365 Flaws Demand Upgrades Now

Veeam has published a fresh batch of security bulletins covering Backup & Replication 13, Veeam Backup for Microsoft 365, Veeam Agent for Linux and Veeam ONE, and two of the fixes are rated critical. The headliner, CVE-2026-108142 (CVSS v4.0 9.1), lets an unauthenticated attacker bypass authorization on the CDP Coordinator Service of Windows-based Backup & […]

Continue Reading
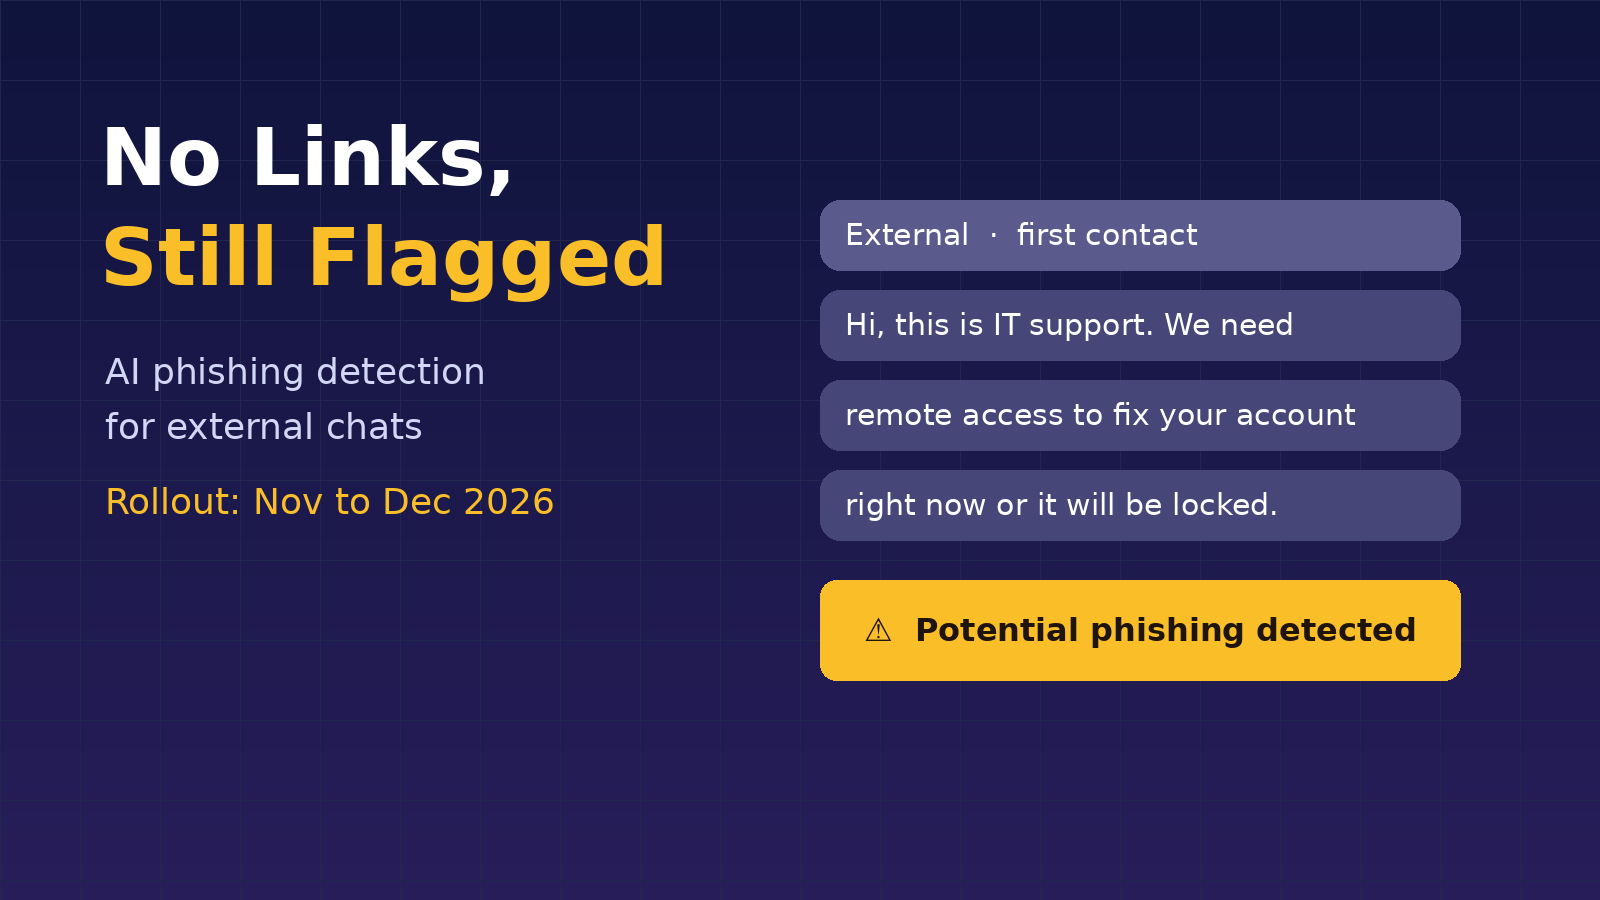
Illustration of an external Teams chat impersonating IT support with a Potential phishing detected warning

Microsoft Teams AI Phishing Detection: Catching Social Engineering With No Malicious Links

Microsoft is bringing AI-powered, context-aware phishing detection to Microsoft Teams, and it is aimed squarely at the attacks that sail past traditional filters: social engineering chats that carry no malicious link, no file and no payload, just a convincing story. Announced in Microsoft 365 Message Center post MC1519866 on October 21, 2026, the feature analyzes […]

Continue Reading
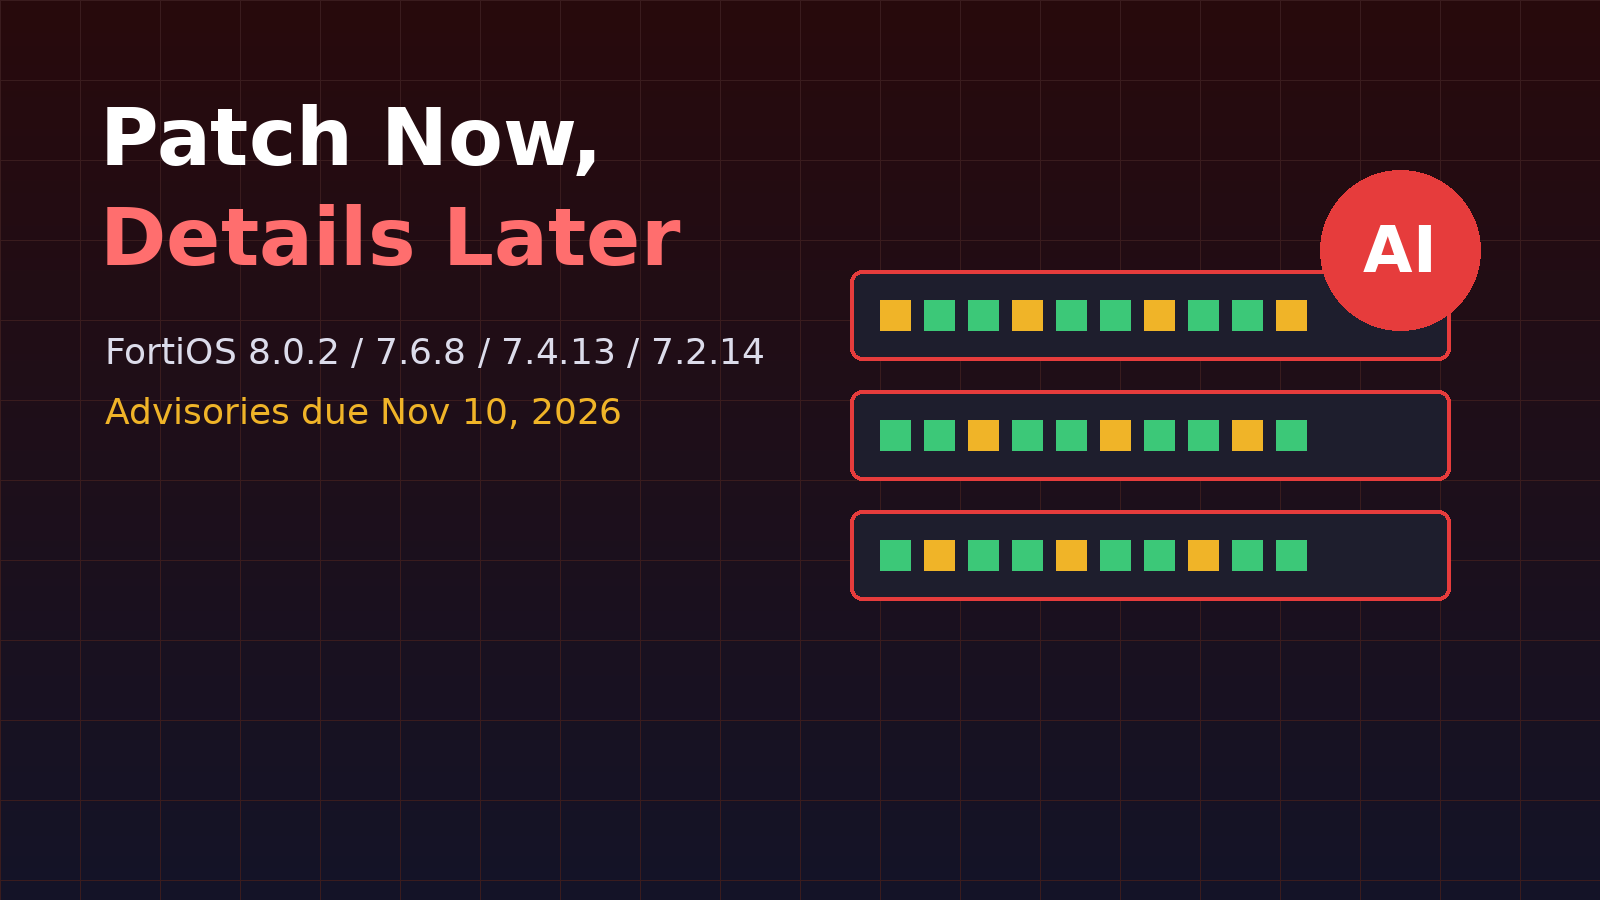
Illustration of firewall appliances with an AI badge and the text Patch Now, Details Later with FortiOS fixed versions

Fortinet’s AI-Found FortiOS Flaws: Patch Now Because the Details Drop November 10

Fortinet has shipped a coordinated wave of security hardening releases for FortiOS, FortiManager, FortiAnalyzer, FortiMail and FortiAuthenticator, fixing critical and high-severity vulnerabilities that were uncovered with the help of frontier AI models, and it is doing something unusual: the fixes went out on October 22, 2026, but the CVE IDs, CVSS scores and technical advisories […]

Continue Reading
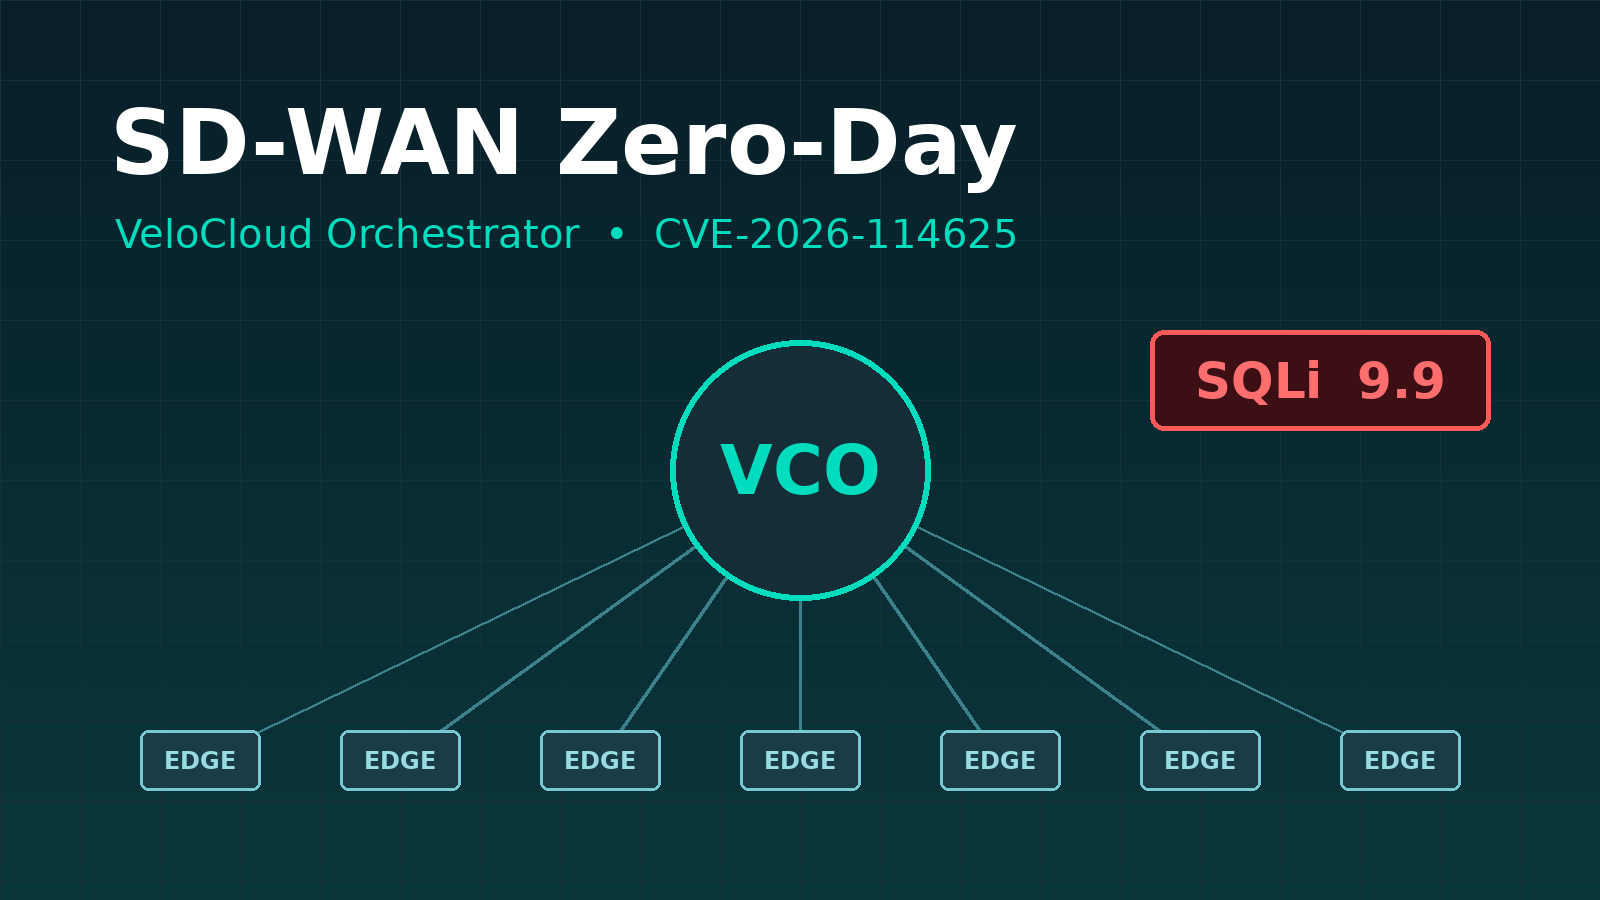
Illustration of a VeloCloud Orchestrator connected to SD-WAN edges with a critical SQL injection warning

Arista VeloCloud Orchestrator Zero-Day CVE-2026-114625: Read-Only Users Become SD-WAN Superusers

Network teams running their own SD-WAN management plane have another urgent patch on the list. On October 22, 2026, Arista Networks disclosed CVE-2026-114625, an actively exploited SQL injection flaw in on-premises VeloCloud Orchestrator (VCO), the web portal used to configure and manage VeloCloud SD-WAN edges and gateways. The bug scores 9.9 on CVSS v3.1 and […]

Continue Reading
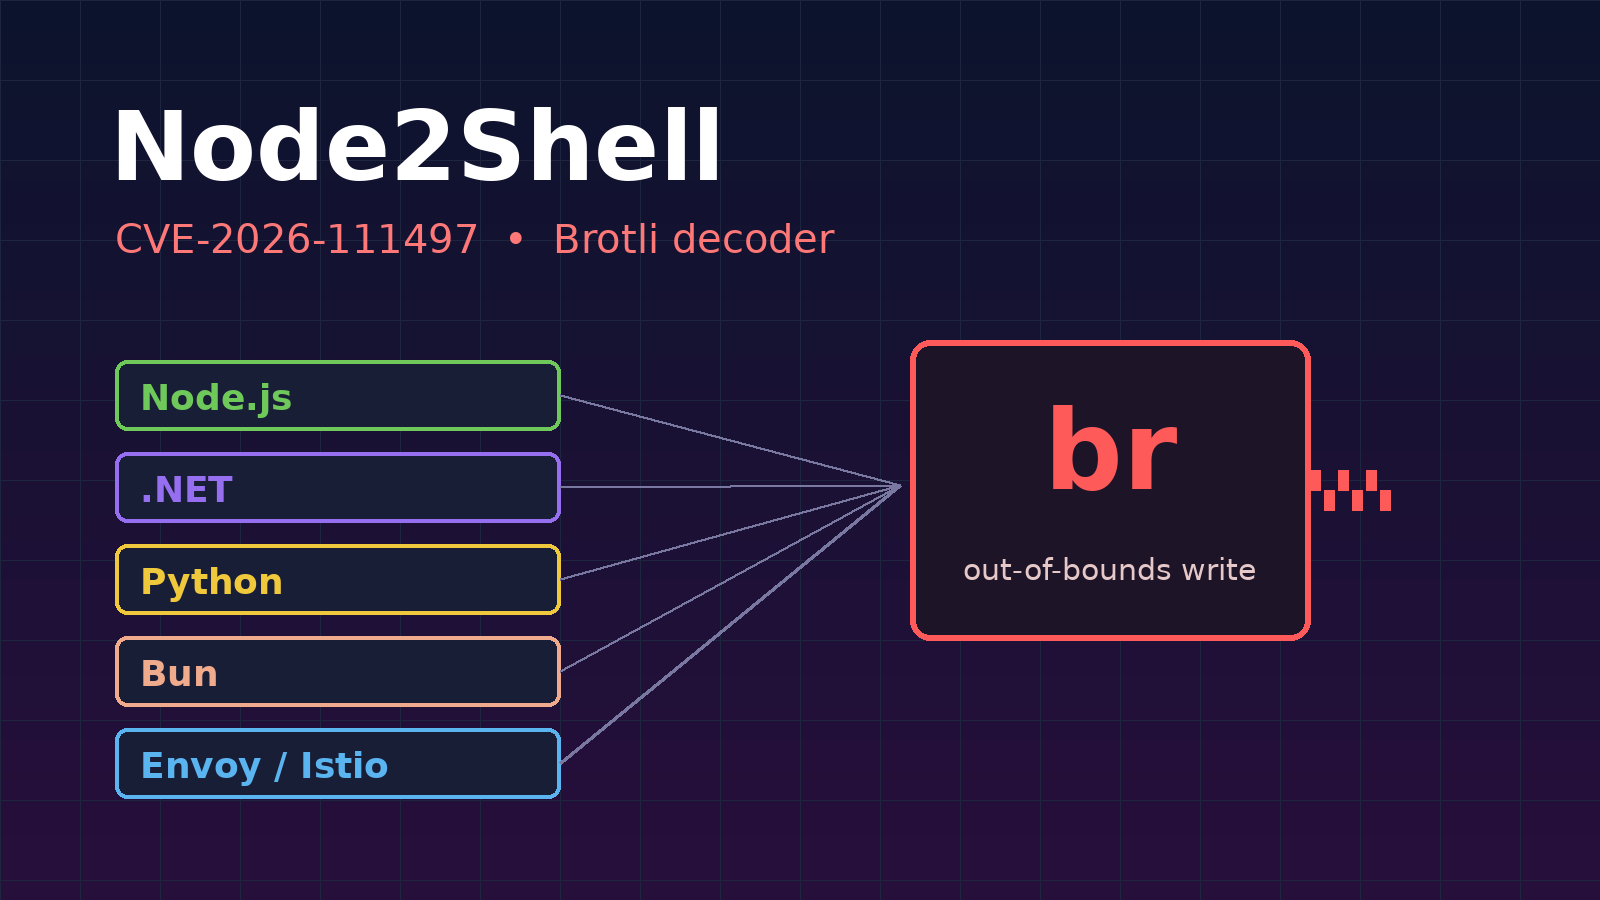
Illustration of the Node2Shell Brotli decoder flaw affecting Node.js, .NET, Python, Bun, Envoy and Istio

Node2Shell Brotli Flaw CVE-2026-111497: Microsoft Rushes Out-of-Band .NET Fixes as Node.js and Python Patch Up

A single bug in one of the web’s most widely embedded compression libraries has turned into a cross-platform patching scramble. CVE-2026-111497, nicknamed Node2Shell, is an out-of-bounds write in Google’s Brotli decoder that affects Brotli 1.0.3 through 1.2.0 and carries a CVSS v4 score of 9.2. Node.js and two Python packages shipped fixes last week, and […]

Continue Reading