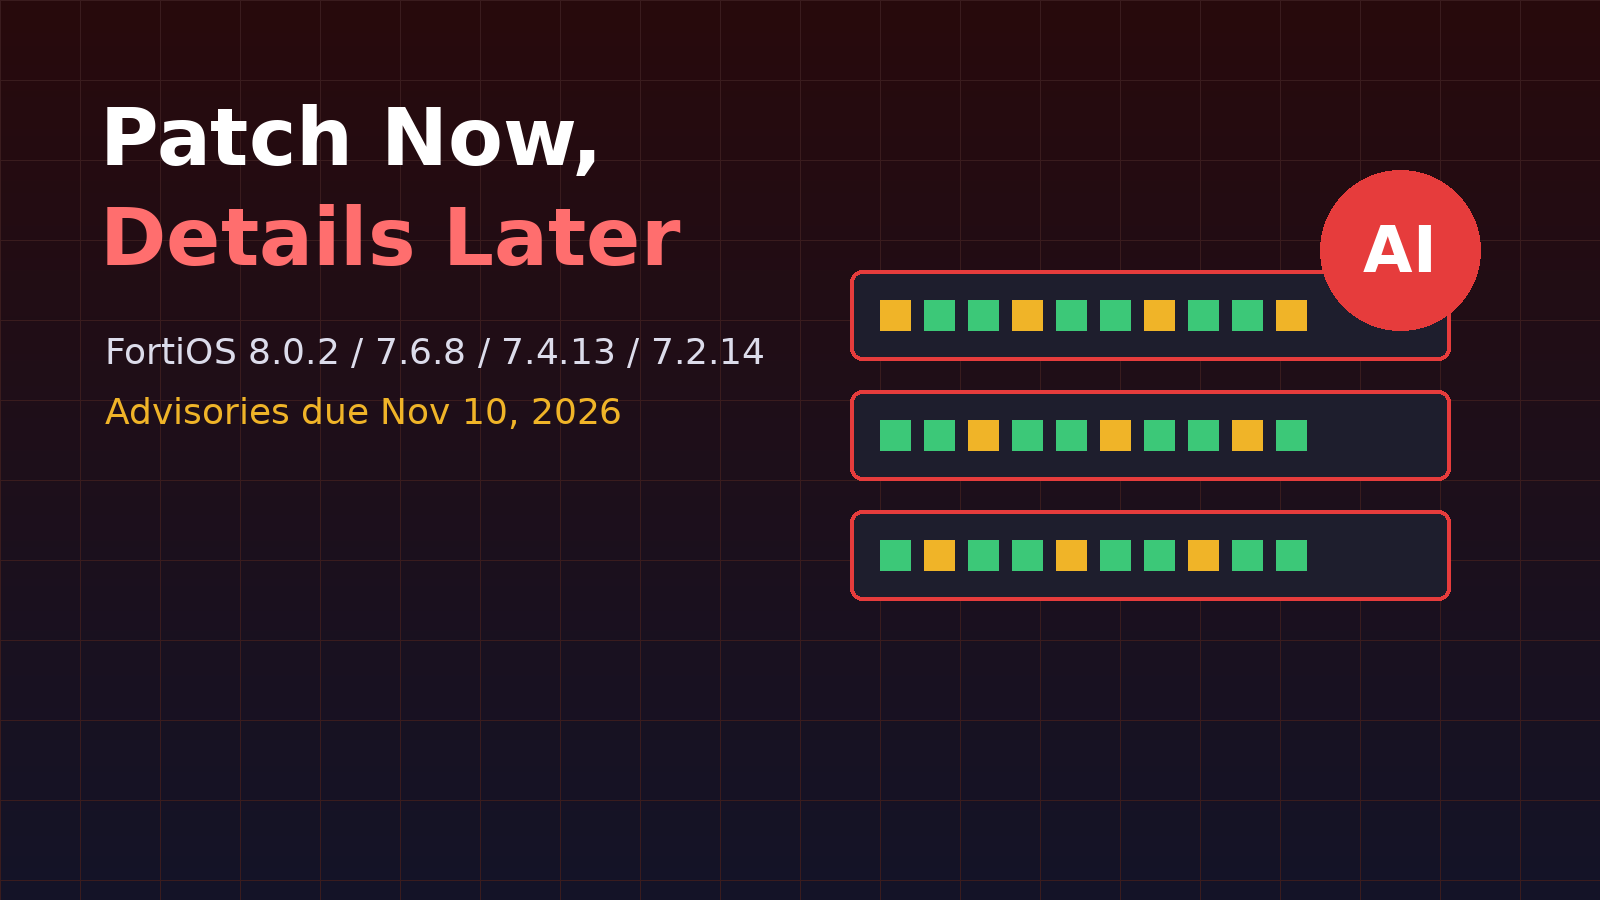
Illustration of firewall appliances with an AI badge and the text Patch Now, Details Later with FortiOS fixed versions

Fortinet’s AI-Found FortiOS Flaws: Patch Now Because the Details Drop November 10

Fortinet has shipped a coordinated wave of security hardening releases for FortiOS, FortiManager, FortiAnalyzer, FortiMail and FortiAuthenticator, fixing critical and high-severity vulnerabilities that were uncovered with the help of frontier AI models, and it is doing something unusual: the fixes went out on October 22, 2026, but the CVE IDs, CVSS scores and technical advisories […]

Continue Reading
Illustration of a VeloCloud Orchestrator connected to SD-WAN edges with a critical SQL injection warning

Arista VeloCloud Orchestrator Zero-Day CVE-2026-114625: Read-Only Users Become SD-WAN Superusers

Network teams running their own SD-WAN management plane have another urgent patch on the list. On October 22, 2026, Arista Networks disclosed CVE-2026-114625, an actively exploited SQL injection flaw in on-premises VeloCloud Orchestrator (VCO), the web portal used to configure and manage VeloCloud SD-WAN edges and gateways. The bug scores 9.9 on CVSS v3.1 and […]

Continue Reading
Illustration of the Node2Shell Brotli decoder flaw affecting Node.js, .NET, Python, Bun, Envoy and Istio

Node2Shell Brotli Flaw CVE-2026-111497: Microsoft Rushes Out-of-Band .NET Fixes as Node.js and Python Patch Up

A single bug in one of the web’s most widely embedded compression libraries has turned into a cross-platform patching scramble. CVE-2026-111497, nicknamed Node2Shell, is an out-of-bounds write in Google’s Brotli decoder that affects Brotli 1.0.3 through 1.2.0 and carries a CVSS v4 score of 9.2. Node.js and two Python packages shipped fixes last week, and […]

Continue Reading

eMudhra CA Key Compromise: Browsers Distrust emSign ECC Root, Patch Your Trust Stores Before October 27

The web’s certificate trust system just had one of its scariest weeks in years. On October 17, 2026, an independent researcher proved that the private keys of eight eMudhra intermediate certificate authorities could be recovered straight from their public certificates, meaning anyone could have forged trusted HTTPS certificates for any website against clients that still […]

Continue Reading

GitLab CVE-2026-110264: CVSS 10 Unauthenticated RCE Puts Self-Managed Servers on the Clock

GitLab has shipped an emergency critical patch release for CVE-2026-110264, an integer overflow in its regular-expression compiler that carries the maximum CVSS score of 10.0 and could let an unauthenticated attacker execute arbitrary code on a self-managed GitLab server. Released on October 21, 2026 as versions 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10 and 18.11.13, the […]

Continue Reading

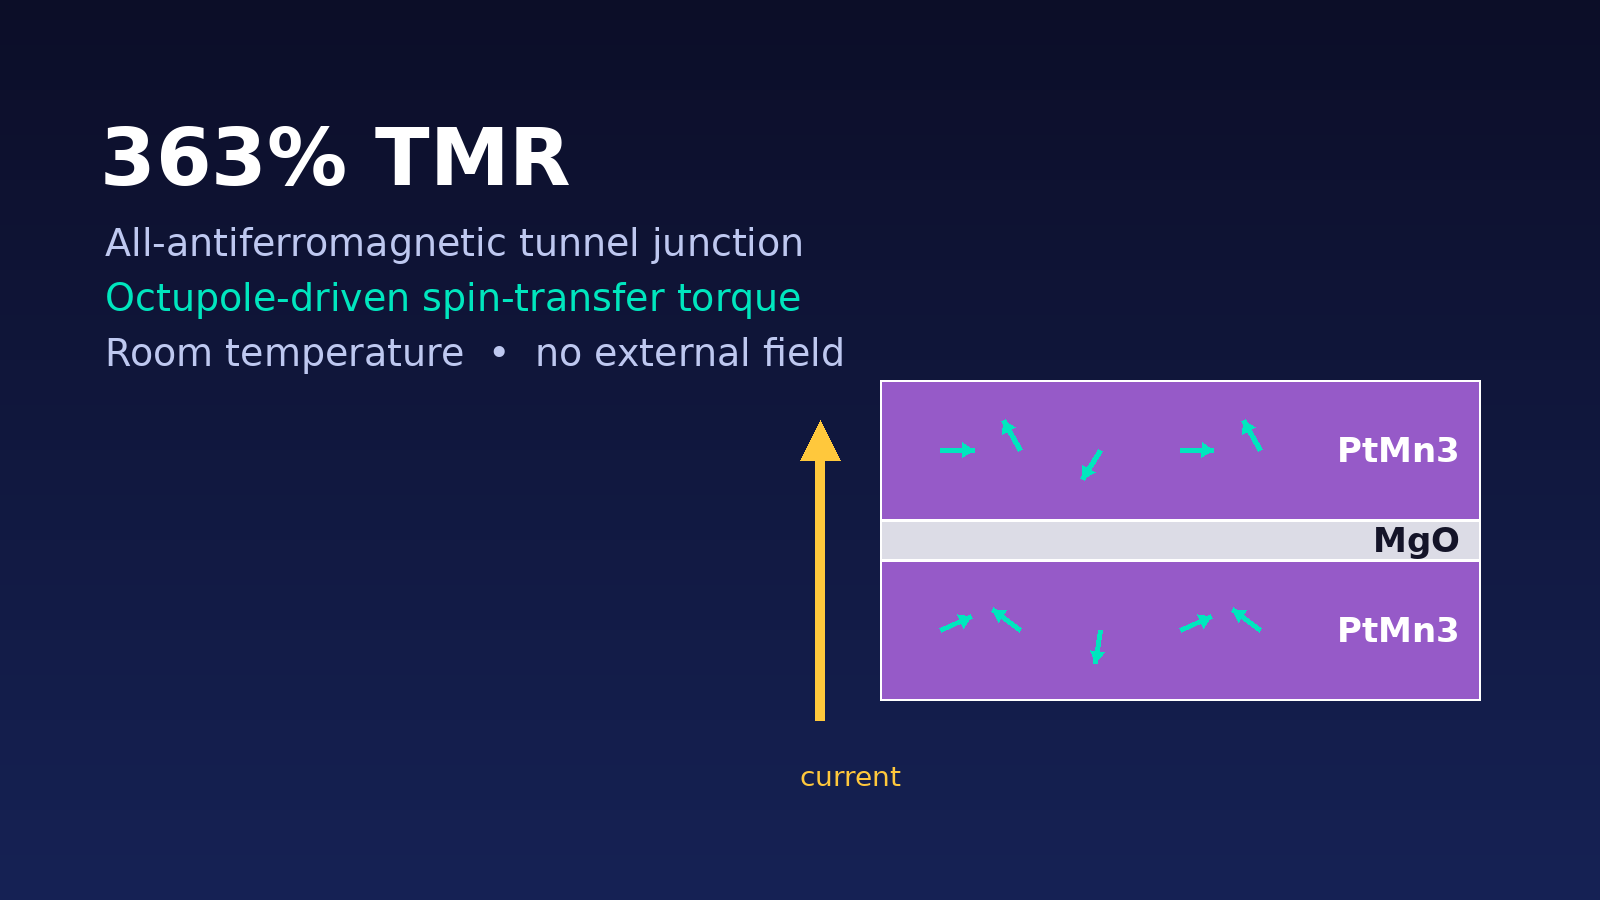
Antiferromagnets Finally Take Orders: Northwestern’s Octupole Spin Torque Opens a Path to Magnet-Proof MRAM

A team led by Northwestern University’s Pedram Khalili reported in Nature on October 21, 2026 that it has electrically written and read data in a magnetic memory cell built entirely from antiferromagnets, materials long thought to be nearly impossible to control with current. The researchers built nanoscale all-antiferromagnetic tunnel junctions (AATJs) from two layers of […]

Continue Reading

How to Harden Your VPN and Firewall Edge: A Step-by-Step Checklist for IT Pros

The VPN gateway has become ransomware’s favorite front door. On October 19, 2026, Palo Alto Networks’ Unit 42 confirmed that the Qilin and Inc ransomware operations are exploiting CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass that was added to CISA’s Known Exploited Vulnerabilities catalog back on May 13, 2026, to open VPN sessions without valid MFA, […]

Continue Reading

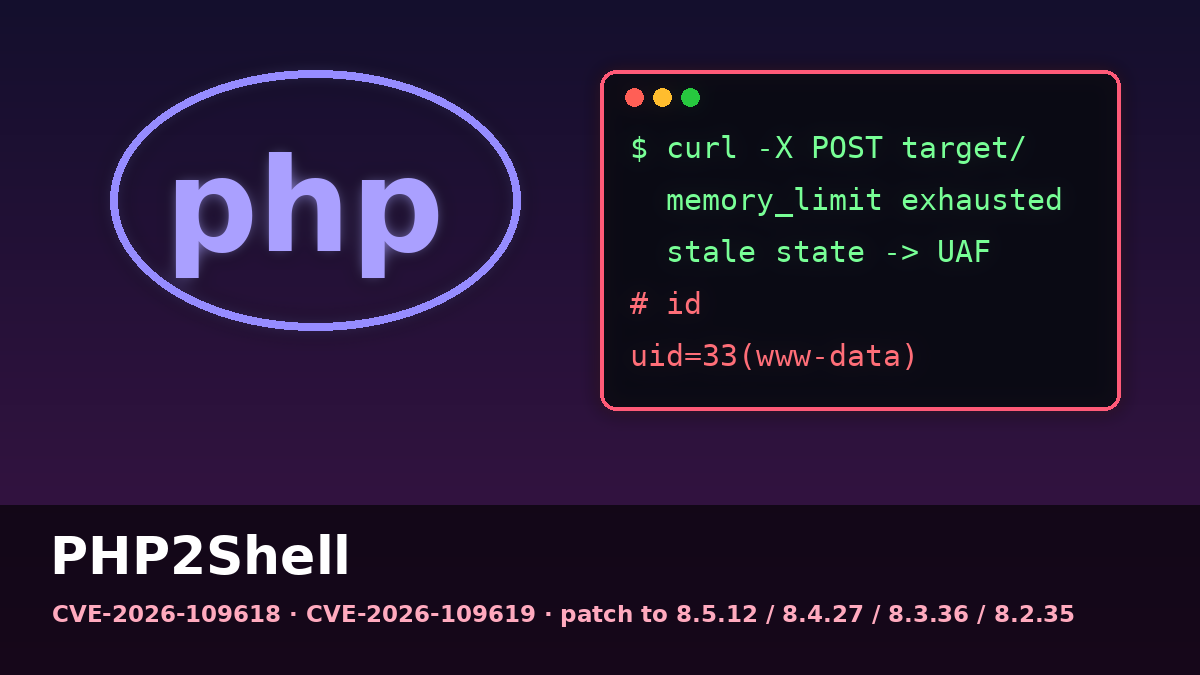
PHP2Shell: Critical PHP Flaws CVE-2026-109618 and CVE-2026-109619 Enable Unauthenticated RCE, Patch Now

On October 21, 2026, the PHP project shipped emergency releases PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to fix two critical flaws in the PHP engine itself: CVE-2026-109618 and CVE-2026-109619, together dubbed PHP2Shell. Both are rated CVSS v4.0 9.2 by the PHP security team and can allow unauthenticated remote code execution, independent of the application running […]

Continue Reading