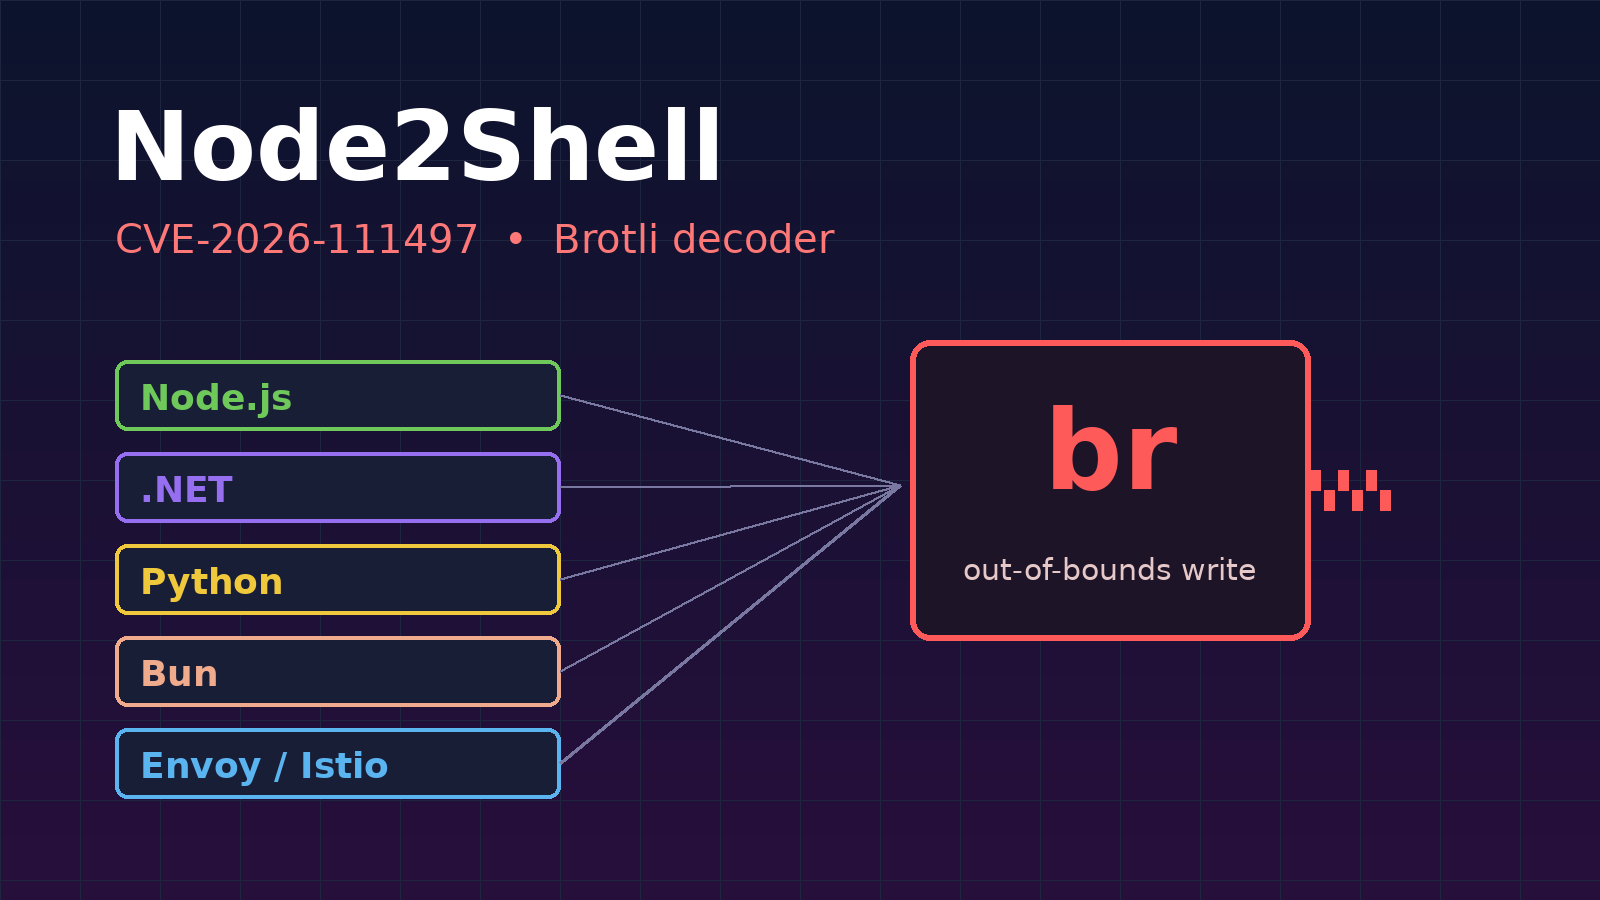
Illustration of the Node2Shell Brotli decoder flaw affecting Node.js, .NET, Python, Bun, Envoy and Istio

Node2Shell Brotli Flaw CVE-2026-111497: Microsoft Rushes Out-of-Band .NET Fixes as Node.js and Python Patch Up

A single bug in one of the web’s most widely embedded compression libraries has turned into a cross-platform patching scramble. CVE-2026-111497, nicknamed Node2Shell, is an out-of-bounds write in Google’s Brotli decoder that affects Brotli 1.0.3 through 1.2.0 and carries a CVSS v4 score of 9.2. Node.js and two Python packages shipped fixes last week, and […]

Continue Reading
eMudhra CA Key Compromise: Browsers Distrust emSign ECC Root, Patch Your Trust Stores Before October 27

The web’s certificate trust system just had one of its scariest weeks in years. On October 17, 2026, an independent researcher proved that the private keys of eight eMudhra intermediate certificate authorities could be recovered straight from their public certificates, meaning anyone could have forged trusted HTTPS certificates for any website against clients that still […]

Continue Reading

GitLab CVE-2026-110264: CVSS 10 Unauthenticated RCE Puts Self-Managed Servers on the Clock

GitLab has shipped an emergency critical patch release for CVE-2026-110264, an integer overflow in its regular-expression compiler that carries the maximum CVSS score of 10.0 and could let an unauthenticated attacker execute arbitrary code on a self-managed GitLab server. Released on October 21, 2026 as versions 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10 and 18.11.13, the […]

Continue Reading

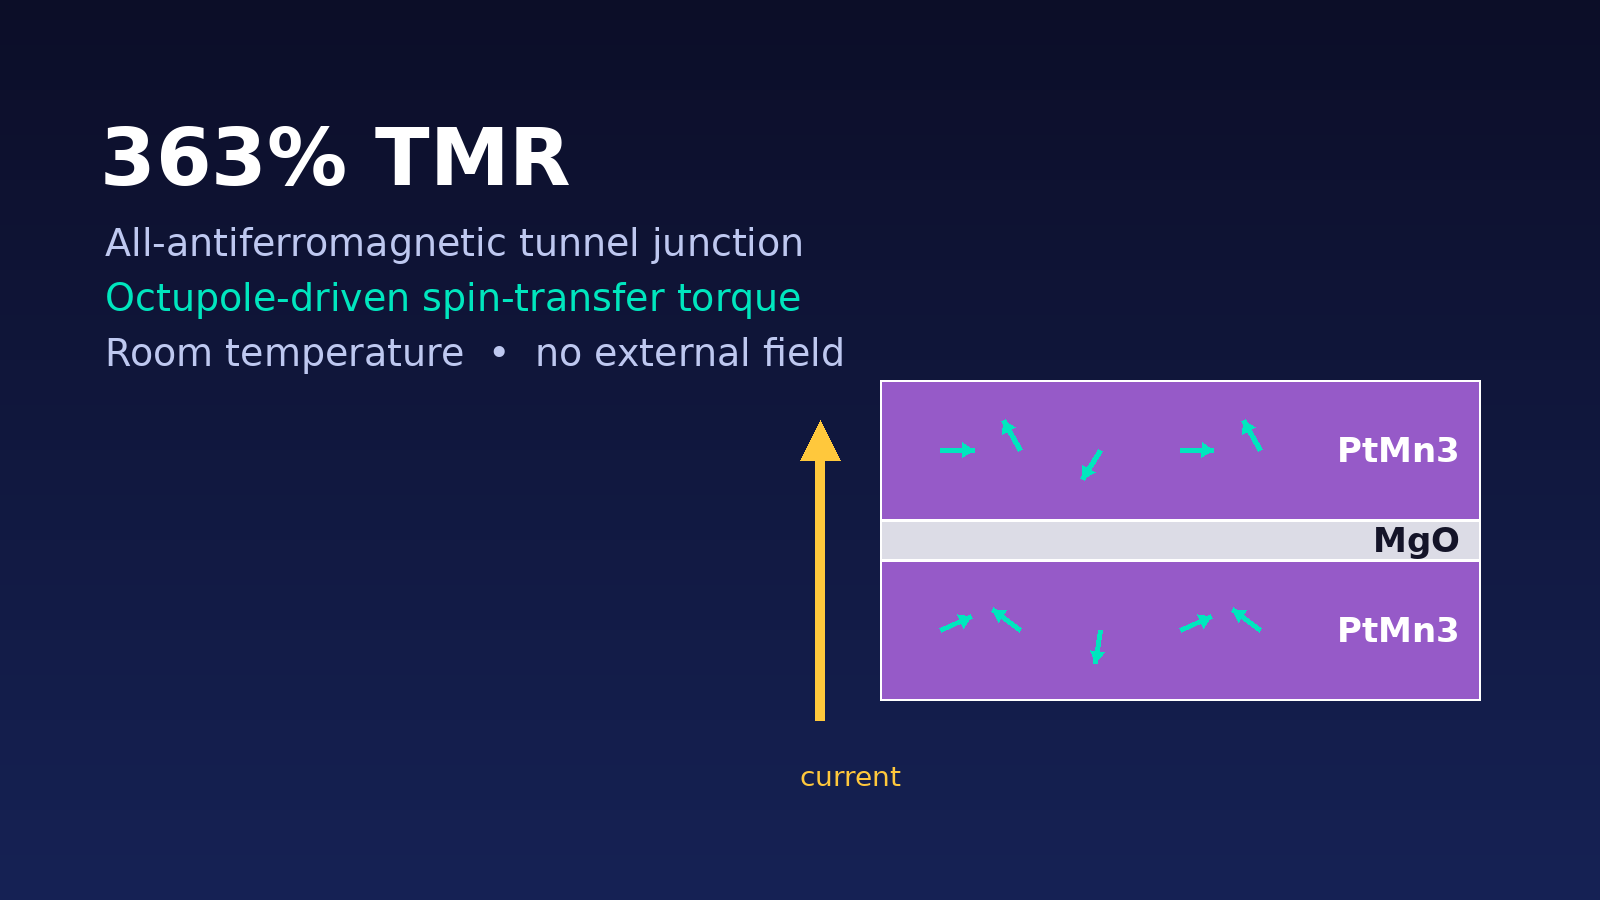
Antiferromagnets Finally Take Orders: Northwestern’s Octupole Spin Torque Opens a Path to Magnet-Proof MRAM

A team led by Northwestern University’s Pedram Khalili reported in Nature on October 21, 2026 that it has electrically written and read data in a magnetic memory cell built entirely from antiferromagnets, materials long thought to be nearly impossible to control with current. The researchers built nanoscale all-antiferromagnetic tunnel junctions (AATJs) from two layers of […]

Continue Reading

PHP2Shell: Critical PHP Flaws CVE-2026-109618 and CVE-2026-109619 Enable Unauthenticated RCE, Patch Now

On October 21, 2026, the PHP project shipped emergency releases PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to fix two critical flaws in the PHP engine itself: CVE-2026-109618 and CVE-2026-109619, together dubbed PHP2Shell. Both are rated CVSS v4.0 9.2 by the PHP security team and can allow unauthenticated remote code execution, independent of the application running […]

Continue Reading
Illustration of a VPN gateway with a cracked padlock and MFA shield as red intrusion lines flow toward virtual servers

PAN-OS GlobalProtect Flaw CVE-2026-0257: Qilin and INC Ransomware Bypass MFA and Pivot to vCenter

Five months after it was patched, a PAN-OS GlobalProtect authentication bypass has become one of ransomware’s favorite front doors. In an update published October 19, 2026, Palo Alto Networks’ Unit 42 said the Qilin (tracked as Spikey Scorpius) and INC (Tarnished Scorpius) ransomware operations are actively exploiting CVE-2026-0257, a CVSS 7.8 flaw in the GlobalProtect […]

Continue Reading

ConnectWise Cloud Backup Supply-Chain Attack: What MSPs Must Check in Every Microsoft 365 Tenant

Since Friday, October 16, 2026, managed service providers have been scrambling after attackers got hold of a credential belonging to ConnectWise Cloud Backup, the Microsoft 365 backup service formerly sold as SkyKick, and used it to sign in to customer tenants as the trusted backup app itself. Huntress first confirmed unauthorized sign-ins in 162 tenants, […]

Continue Reading